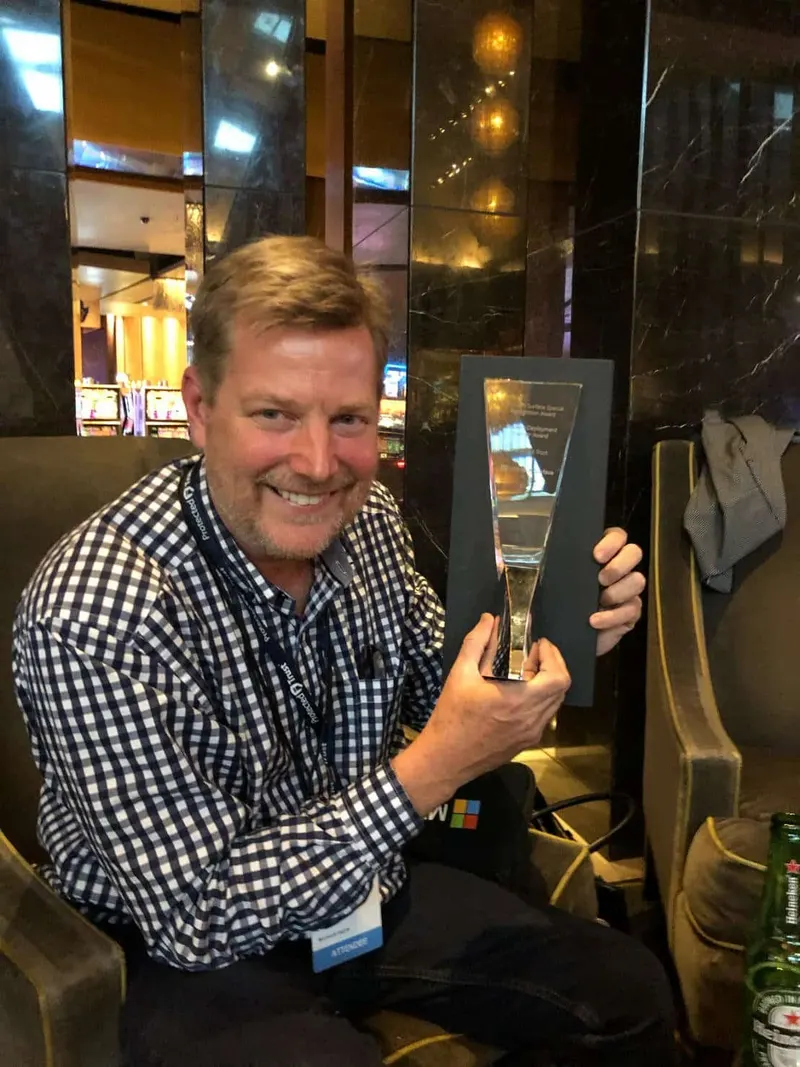
In 2020 I ran a phishing attack on camera, from the attacker's chair and then from the victim's, to show how little it takes to give away a password. Afterward we wrote down the signs that would have stopped it. The tools have changed since then. The signs have not.
- Someone you have never heard from wants you to click or change something. A new sender plus a request to act is the shape of almost every phish. Do not reply to the email to check; the attacker answers replies. Call the person, or walk over.
- The address is almost right. An extra letter, a missing one, .co instead of .com, a dash where there was none. We read words as shapes, and the attacker knows it. Read the address letter by letter.
- It is urgent. Your account will close, the payment will bounce, the boss needs it before the meeting. Urgency exists to stop you thinking. Slow down, and look for the other signs.
- The link says one place and goes to another. On a computer, rest the pointer on it and read the real destination. On a phone, press and hold. If you want the real site, type its address yourself or use your bookmark.
- For the technical: the headers do not match. Where a message really came from is in its headers, and a sending address can be faked with characters that look like English letters and are not. Send the message to us and we will read them.
- A page asks you to sign in. Look at the address bar before you type anything. If the address is not the service you expected, close it. Real services rarely email you a sign-in link out of the blue.
- The page looks like an old version of the site. Attackers copy a sign-in page once and use it for years. If it looks dated, it is a copy.
- The browser warns you. A warning from the browser is a stop sign. The reverse is no longer true: the lock icon only means the connection is encrypted, and attackers have certificates too.
- You signed in, and it bounced you to the real site to sign in again. That blip was the handoff. The fake page took your password and sent you on to the real one so you would not notice. Change the password now, from a device you trust, and tell us.
What to do when one gets through: do not forward it around the office, send it to us, and if you typed a password anywhere, say so in the first sentence. Nobody is ever in trouble for reporting a phish. People are only in trouble for the one they kept quiet about.
Short, regular training is in every plan, with messages like these sent to your own people so the first phish they fall for is ours. Security awareness training.
Let's talk
Thirty minutes with a real person.
Tell us what's going on with your technology, what's working and what isn't. We'll listen, ask a few questions, and tell you honestly whether we're the right fit. No slides, no pitch. If we can help, we'll say how. If we can't, we'll point you to someone who can.
Reach out, any way you like. A real person takes it from there.
Based in downtown Winter Haven since 1996, with offices in Orlando, Tampa, St. Petersburg, and Miami, serving businesses across Florida.